OmniARP Command Surface
Policy Locked
Cross-Layer Incident Graph
Noisy-OR CorrelationKeep incident intelligence, root-cause correlation, and remediation approvals fully inside your firewall with governed, audit-ready autonomy.
OmniARP Command Surface
Cross-Layer Incident Graph
Noisy-OR CorrelationTrust metrics
Self-hosted deployment keeps operational context inside your environment.
Every high-impact action can be rehearsed and approved before execution.
Correlate signals across databases, Kubernetes, and infrastructure in one view.
Signed workflows and tamper-evident records support regulated operations.
Platform capabilities
Core product modules designed for SRE, infrastructure, and governance teams that need deterministic operations and private AI reasoning.
Unify infrastructure, database, and platform signals into one cause-and-effect view.
Surface the most likely failure path instead of flooding teams with parallel noise.
Keep AI actions inside explicit control rails rather than opaque autonomy.
Validate proposed remediation in a synthetic clone before production approval.
Preserve who approved what, when, and under which evidence chain.
Run inside your own environment without depending on external AI APIs.
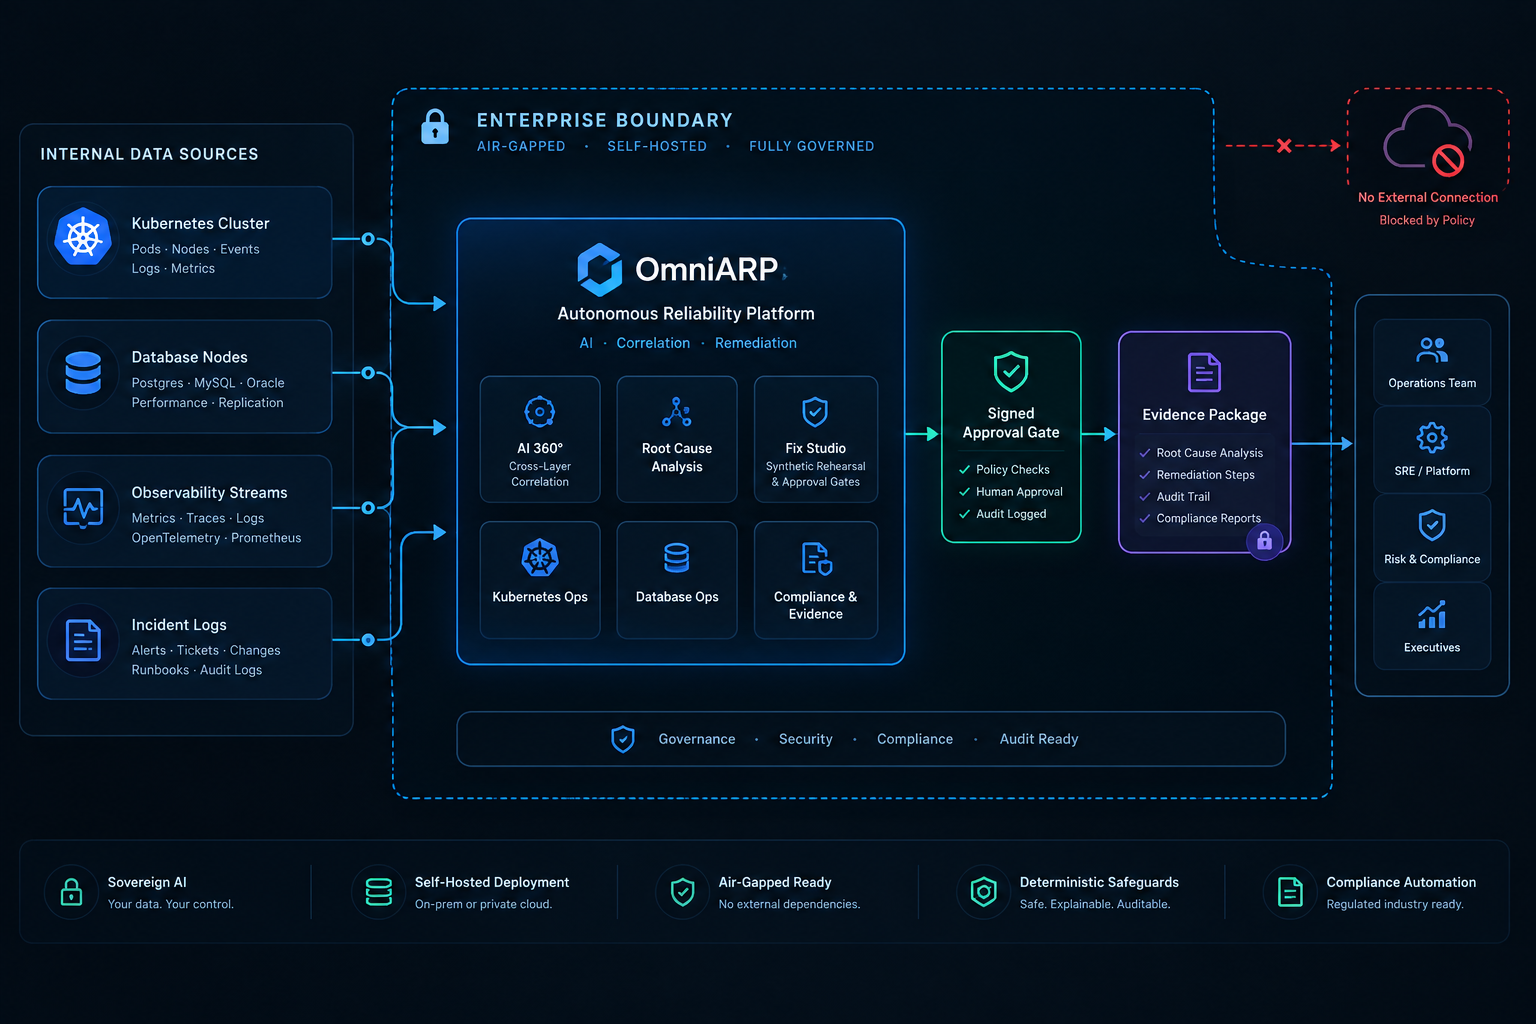
Governance Architecture
OmniARP keeps analysis, approvals, and remediation evidence inside enterprise control planes.
Contained enterprise boundary
Signed approval + evidence flow
Operational sequence
Deploy
Install OmniARP inside your environment with a standard enterprise-ready footprint.
Correlate
Unify noisy infrastructure and database signals into a likely failure path.
Rehearse
Test remediation in a synthetic clone before anyone touches production.
Approve
Apply controlled change through governed review and signed evidence.
Operator voices
Real operators and governance stakeholders describe why OmniARP feels controlled, auditable, and deployment-ready in enterprise environments.
“OmniARP felt built for teams that cannot gamble on opaque automation. We could see the likely cause, rehearse the change, and move with control.”
“The strongest signal for us was private deployment. We were able to evaluate the platform without opening a new data-exposure conversation.”
“The approval path and evidence model made the difference. It gave us a practical way to review AI-driven actions without slowing the team to a halt.”
Security FAQ
Direct answers to the most common security, governance, and deployment questions from enterprise infrastructure leaders.
No. OmniARP is designed for private deployment, so teams can evaluate and operate it without routing incident context to external AI services.
High-impact actions can follow governed approval gates and rehearsal steps before production execution, with deterministic fallback paths where needed.
Yes. OmniARP is positioned around signed workflows and tamper-evident operational records that support internal review and audit preparation.
Enterprise teams can start with a contained deployment path suited to infrastructure, database, and Kubernetes-heavy environments.
Yes. It is designed to give operators faster clarity while giving security and governance teams the controls they need to sign off responsibly.